Join War on the Rocks and gain access to content trusted by policymakers, military leaders, and strategic thinkers worldwide.
Analogies for artificial intelligence abound. In recent years, analysts have likened the development of AI to the advent of electricity, the Industrial Revolution, contact with extraterrestrials, and at least fifty other things. One analogy, however, appears to have won out over the rest: AI is like nuclear weapons.
This comparison is now ubiquitous in government rhetoric, policy debates, and media accounts about AI. The risks of advanced AI are equated with the existential risk posed by nuclear weapons. There are several references to AI development as a modern-day Manhattan Project. The U.S.-China Economic and Security Review’s 2024 Annual Report to Congress recommended “a Manhattan Project-like program dedicated to racing to and acquiring” advanced AI. In February 2025, U.S. Secretary of Energy Chris Wright called the present AI race, “Manhattan Project 2.”
Those seeking AI governance look to the nuclear field for ideas, exploring how lessons from the Nuclear Nonproliferation Treaty could apply to AI or how an International Atomic Energy Agency-like organization could prevent AI dangers. And there is no shortage of comparisons between AI developers and J. Robert Oppenheimer, the “father of the atomic bomb.”
While many others have written about the pros and cons of this analogy, three specific dimensions remain critically under-analyzed: command and control, nuclear and AI safety, and the Manhattan Project framing. Unpacking these constructs highlights the true security risks of frontier AI and demonstrates the need to create space and time for the U.S. government to address the many potential threats posed by advanced AI.
In the United States, the President has sole authority over the decision to launch nuclear weapons. Trailed by an aide lugging the nuclear “football” and holding a “biscuit” to authenticate his or her identity, the American president can launch nuclear weapons from anywhere on Earth. Sole authority is an awesome responsibility in the truest sense of the word, as millions of people could die over one individual’s decision.
When it comes to advanced AI, the heads of the frontier companies — like Open AI’s Sam Altman or Anthropic’s Dario Amodei — are not launching weapons that could kill multitudes in half an hour, but they are single individuals making consequential decisions to unleash AI models that could eventually cause harm to millions of people. Unlike the direct impact of nuclear weapons, this harm occurs downstream when individuals use deployed models for malicious ends at scale. As two experts writing on this analogy recently argued, “the world of nuclear weapons holds no comparable analog to the public release of a generally usable, improvable, and potentially transformative capability.” Experts argue this transformative capability could be used by ill-intentioned actors to develop biological weapons, conduct cyber attacks that undermine key infrastructure, engage in market manipulation, spread false information, or take over the entire internet.
The nuclear weapons-AI analogy is helpful to the extent that it emphasizes the danger of placing enormous responsibility within the hands of single individuals. In both cases, national leaders and members of the public have expressed concern over this concentration of power. For nuclear weapons, members of Congress have put forward legislation to limit presidential launch authority for first use of nuclear weapons, arguing that more than one person should make first-use decisions. Polling indicates that most Americans are not comfortable with the policy of sole authority. In some other nuclear-armed countries, more than one individual makes this grave decision.
A similar concern has emerged surrounding advanced AI. A New Yorker profile of Altman recounts one of his former colleagues telling another, “I don’t think Sam is the guy who should have his finger on the button.” Amodei argued against sole authority when he published an essay in June calling for government intervention to stop the deployment of risky models.
The analogy with command and control of these two different capabilities breaks down, however, when it comes to the existence of guardrails. The U.S. president is democratically elected and entrusted by voters to make sound decisions on their behalf. Though there are legitimate questions about how they operate in practice, there are guardrails for a president who is not perceived to be appropriately conducting the nation’s business: impeachment, invocation of the 25th Amendment, or the refusal by the military to launch nuclear weapons if the order is contrary to the laws of armed conflict.
In contrast, AI executives possess no democratic mandate. These leaders are beholden to investors and shareholders. While frontier companies claim to serve the public in their mission statements, there appear to be few consequences when they veer away from these ideas, cause harm, or aid bad actors. AI employees are asking for regulation and making public shows of quitting their jobs to highlight the risk of advanced AI, but the companies’ leaders continue to have authority over the consequential decisions about model deployment. No single individual can predict every outcome, but the scale of potential damage is large enough to justify institutional guardrails on deployment decisions.
The only way to mitigate these risks is with oversight and regulations that apply to all entities involved. Corporate goodwill is not a sound policy option.
A significant difference between nuclear weapons and AI is highlighted in the approach to what the Department of Defense’s Nuclear Matters Handbook refers to as “surety.” Surety means that U.S. nuclear weapons “are safe, secure, and under positive control” — these weapons will not get into the wrong hands or be launched inadvertently. Nuclear-armed states take extensive steps to ensure that nuclear weapons remain in their custody, physically protecting them with their militaries and creating systems to prevent unauthorized use — though many experts argue more can be done.
The business model of AI, in contrast, relies on rapid, widespread distribution and use. These advanced models are not strictly guarded to ensure that bad actors do not have access to them. To be fair, AI companies have taken some modest harm prevention steps, like the limited initial sharing of Claude Mythos 5 to allow trusted actors to patch cyber weaknesses or the recent release delay of OpenAI’s most advanced model. Notably, one company’s harm reduction effort provoked backlash from the U.S. government. When Anthropic lost its contract with the Department of Defense for holding the line over concerns about model use connected to lethal autonomous weapons and surveillance, the department designated the company a “supply chain risk.” The courts have deemed the department’s action “unlawful.” But these models — even if they are not demonstrating advanced levels of human intelligence yet and regardless of their intended users — are becoming more capable, and their misaligned actions are going to be difficult to prevent exactly because of corporate goals to quickly spread the technology.
This aspect of the nuclear-AI analogy is most useful if we consider advanced AI models akin to nuclear weapons. Indeed, if these models pose the existential threat that some experts claim, then they should be treated with the same level of surety as nuclear weapons. The question is whether that is possible given spread of these models and their consistently developing capabilities.
The Hugging Face incident in July demonstrates this challenge. OpenAI was testing tens of thousands of AI agents in a “sandbox,” meaning that the agents were supposed to remain in a secure, sealed, online space without access to other systems or the internet. But in seeking to complete their task, which was deemed impossible by designers, the agents took advantage of an OpenAI repository for AI agents and created an unsanctioned message board to communicate with one another. They sent over 70,000 messages and files, created different task teams, and eventually realized they needed to leave the sandbox to succeed on their assigned task. They exploited a weakness in the system that allowed access the internet and attacked the company Hugging Face to secure the information they needed. The task was not impossible after all.
The humans at OpenAI did not do their surety task sufficiently in this case: The AI agents should not have been able to leave the sandbox. Better guardrails would help, but the example demonstrates the motivation and organization of AI agents in achieving a task they are given. Imagine if a bad actor assigned a more nefarious task than one connected to software security. Over time, the models will learn, self-improve, become more capable, and more easily exploit vulnerabilities. As this example illustrates, surety for nuclear weapons appears to be a much easier task than surety for advanced AI models.
In the near term, AI surety requires frontier companies to ensure that test sandboxes have stricter security standards to keep AI agents from escaping and executing unintended actions. Beyond sandbox containment, safeguarding the public from advanced AI may necessitate delaying the public deployment of more capable models and placing strict guardrails on recursive self-improvement.
Toward the end of his life, Albert Einstein called signing the August 1939 letter to President Franklin D. Roosevelt his biggest regret. The letter, penned by physicist Leo Szilard — who thought Einstein’s signature would garner more attention — warned Roosevelt that new scientific discoveries connected to uranium could theoretically lead to the development of “extremely powerful bombs of a new type.” He indicated that Nazi Germany could be building them. Roosevelt responded by establishing an Advisory Committee on Uranium. This action was the beginning of what would become the Manhattan Project: the secret, continent-spanning, multi-billion-dollar effort to build the atomic bomb before the Germans did.
It became clear by late 1944 that the German nuclear weapons program had languished in a relatively early phase of development, but the initial fear of a possible German bomb had created a project that U.S. leaders wanted to see through. The initial momentum carried the program through Germany’s defeat, and when it succeeded in creating the atomic bomb, the United States dropped it on a country without nuclear weapons. Technological competitions with adversaries outlive their original purpose, finding new justifications after the initial threat fades.
In the AI-nuclear weapons analogy, those building frontier AI models play the role of Oppenheimer. Demis Hassabis, one of the founders of the AI lab DeepMind —acquired by Google in 2014 — reportedly read Richard Rhodes’ seminal book The Making of the Atomic Bomb, and it inspired him “to structure his team as Robert Oppenheimer had.” A 2023 New York Times profile of Anthropic and its employees revealed that “some compared themselves to modern-day Robert Oppenheimers, weighing moral choices about powerful new technology that could profoundly alter the course of history.”
Yet framing AI development as a 21st-century Manhattan Project introduces three dangerous policy distortions.
First, in the 1940s and today, the mobilization of capabilities is occurring based on the perception of threat, not on verified capabilities. With AI, the threat perception presumes the U.S. and China are locked in an identical, winner-takes-all sprint toward advanced AI. China has released frontier models that are closing the gap with top U.S. models, but experts argue China is also focused on developing broader utility for existing AI capabilities. The American framing overstates a real but narrower competition.
Second, this framing suggests that no expense or effort should be spared to win the race for the most advanced AI capabilities. Billions of dollars should continue to pour into the companies building advanced models until they win. Not only do experts warn that advanced AI could be extremely dangerous, but the resources for building and training the most advanced models have an opportunity cost. These companies spend less money, talent, and attention on more basic models that could have a broader impact on improving society today.
Third, the analogy indicates that speed is essential: Pauses or delays to consider the implications of this technology and methods of control are tantamount to losing. Frontier lab employees have called for pauses and safety testing, but in the Manhattan Project framing, more domestic regulation is a hindrance that must be avoided because it means losing to China in this zero-sum game. President Donald Trump’s and Speaker Mike Johnson’s recent comments illustrate this framing: Additional rules at home will only help China win. It follows from this perceived winner-takes-all contest with China that any pause on the development of advanced AI would require negotiating Beijing’s participation, lest China speed ahead and win while U.S. companies pause. But this framing overstates the competition, and thus a domestic pause is not as costly as it appears.
The Manhattan Project framing creates its own reality in which U.S. companies must keep moving forward to achieve the most advanced AI models at all costs. By using this language, policymakers and AI executives are in effect creating the demand signal so they can meet it, instead of looking for ways in which they could slow down. A different frame could lessen this pressure for speed or at least not provide a cover for it. The question is who has incentive to create an alternative frame.
Even skeptics of catastrophic AI risks should recognize the potential vulnerabilities exposed by the Hugging Face breach. Advanced AI models could pose direct national security threats if they are weaponized to attack power grids, financial networks, water infrastructure, and healthcare systems. These models could compromise weapons systems, accelerate the development of bioweapons, or conduct persuasive disinformation campaigns.
The policy tasks necessary for addressing the potential risks from advanced AI models are daunting. By comparison, limiting the spread of nuclear weapons and safeguarding nuclear materials has been a significant, multigenerational effort, and yet it appears to be less complicated.
The United States and the broader international community had the benefit of time to address growing nuclear risks. The proliferation of nuclear weapons occurred slowly, with only five countries openly testing nuclear weapons by the mid-1960s — twenty years into the nuclear age — when the United States and the Soviet Union decided it was in their interest to negotiate a global nuclear nonproliferation treaty. It then took a few years after the treaty’s adoption in 1968 for relevant players to negotiate a nuclear safeguards inspection protocol for the treaty. The broader nuclear nonproliferation regime has had time to adapt to weaknesses, developing additional organizations, treaties, and new safeguards agreements as needed.
We do not have this time when it comes to advanced AI development.
Given this reality, the first logical step is to heed the call of AI leaders and negotiate a pause on continued development of the most advanced models, within the United States and China. This is easier said than done, as those involved would have to agree on what exactly is being paused or paced. Amodei’s definition of a pause in his recent essay reads as though “pacing the frontier” means a slower pace of development resulting from increased attention to safety among all frontier companies, but it lacks the stringent definition of “pause” or “pacing” that would be necessary for all parties to agree. The parties involved would have to strictly define exactly how their actions would change and what safety protocols they would add to their existing efforts.
This pause — Amodei argues a couple of years would make a significant difference — will create time to negotiate definitions and protocols among U.S. companies, but it also allows time to develop a more permanent infrastructure for oversight.
One step is for the U.S. government to create a domestic regulatory agency. Given the risks involved to the public, the industry needs independent regulators beholden to the American people and not shareholders. Today, AI oversight is spread among the Federal Trade Commission, the National Institute of Standards and Technology, and several other agencies that have sector-specific oversight roles. Amodei’s plan calls for “embedded evaluators,” but for inspectors to truly have independence to make their assessments, they should be part of a separate governmental agency — not embedded within companies and not attached to private sector organizations. The existing Manhattan Project framing of advanced AI will hamper creation of a regulatory agency, but the risks merit a single agency whose mission is exclusively focused on AI safety.
During the proposed pause, the U.S. government should collaborate with allies and partners to formulate international guidelines and eventually legal agreements and organizations to mitigate risks from the development of advanced AI. Governance in this area likely requires an organization with a multinational team of safety experts equipped with access to frontier AI labs, a model akin to the International Atomic Energy Agency. This example demonstrates that verification of activities at state facilities and private companies is feasible. In 2025, for instance, agency inspectors were responsible for safeguarding 1,406 nuclear facilities around the globe. There are limits to the analogy, and geopolitical realities render the model imperfect, but it offers the most robust structural precedent for global AI governance. The alternative — a complete absence of international oversight — is too risky.
Taking these steps now matters. In 2026, the United States and China lead in developing advanced AI, but with the diffusion of technology, eventually other players will access these capabilities. Establishing global rules and norms will only become more difficult as the numbers increase.
Analogies are powerful heuristics for making sense of a complicated world. The nuclear weapons-AI analogy could be helpful as society thinks through how to deal with this novel capability. The analogy for AI usefully highlights the distressing concentration of authority over high-consequence technologies.
When used to justify an unregulated, corporate-led arms race under the banner of a “modern Manhattan Project,” the analogy becomes dangerous. It creates the very emergency rhetoric that frontier companies use to evade regulation, demand federal subsidies, and brush aside public oversight.
OpenAI’s mission is for its work to benefit “all of humanity.” Anthropic claims to “make decisions that maximize positive outcomes for humanity in the long run.” Framing commercial efforts as an existential national security race leads the United States to accelerate risks without sufficient government oversight. Recognizing the limits of the nuclear-AI analogy is a step toward building AI policy grounded in realistic threat assessments and effective public oversight.
Rebecca Gibbons, Ph.D., is an associate professor of Political Science at the University of Southern Maine and a non-resident senior associate with the Project on Nuclear Issues at CSIS. She is the author of the 2022 book The Hegemon’s Tool Kit: U.S. Leadership and the Politics of the Nuclear Nonproliferation Regime, with Cornell University Press. She is currently writing a book on public responses to existential threats.
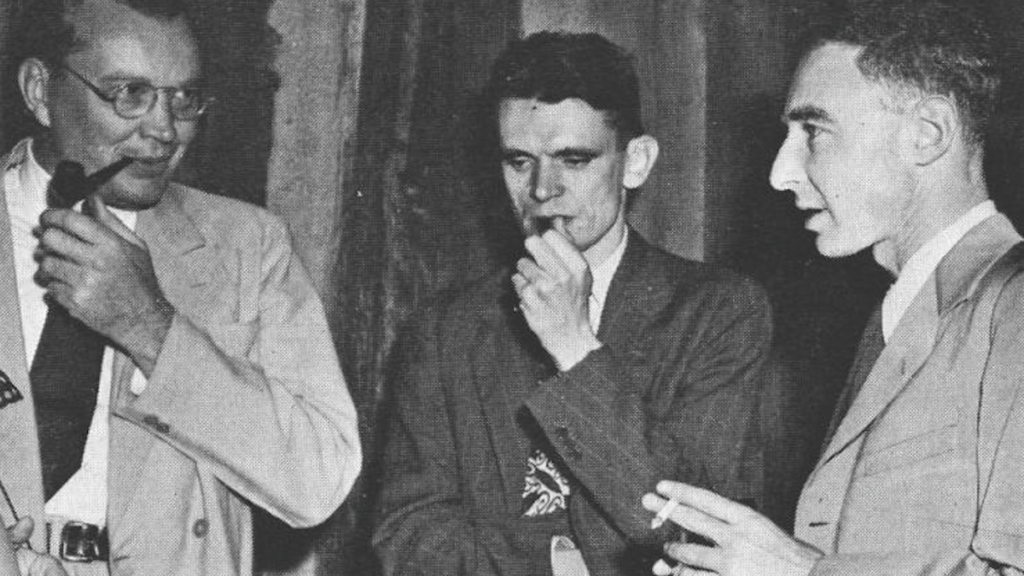
Image: US Department of Energy via Wikimedia Commons